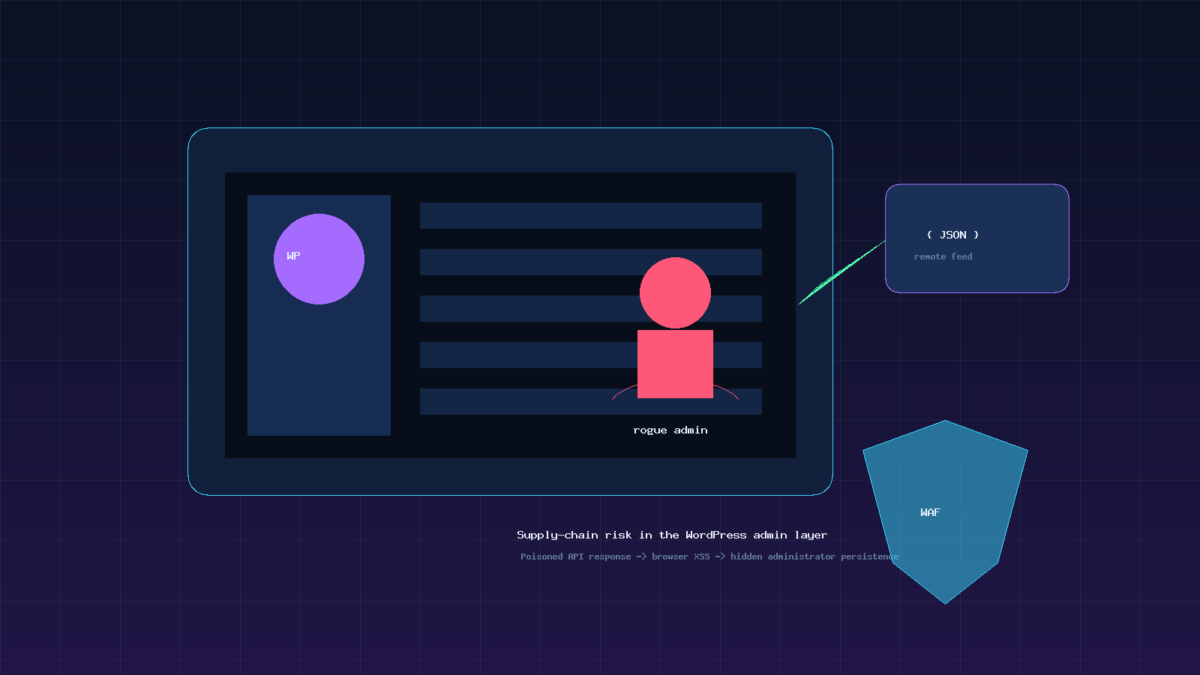
A compromised vendor-side feed in the BdThemes WordPress plugin ecosystem is a reminder that the browser session of a site administrator can become part of the attack surface, even when no plugin update is being installed.
BleepingComputer reported on August 10 that an attacker modified a remote JSON feed used by BdThemes products to deliver malicious JavaScript inside WordPress admin pages. The report says the code used an authenticated administrator session to create rogue admin accounts and attempted persistence through a fake plugin and webshell.
The affected ecosystem matters because BdThemes builds web-design tools used on production WordPress sites, including Element Pack, Prime Slider, Ultimate Post Kit, Pixel Gallery and Ultimate Store Kit. BleepingComputer, citing Defiant’s Wordfence research, said the free Element Pack plugin alone showed more than 100,000 active WordPress.org installations, while BdThemes advertises more than 350,000 active installs across its portfolio.
Why hosts should care
This is not the usual “update the vulnerable plugin” story. The reported entry point was a poisoned API response shown to administrators in wp-admin, with the malicious payload executing when a logged-in admin opened an injected page. That makes the incident closer to a supply-chain and control-plane problem: a remote vendor asset can turn into code running with the privileges of a trusted site operator.
For hosting providers and agencies, the practical checklist is straightforward: review WordPress administrator accounts for unknown users, look for suspicious or newly created plugins, check for unexpected PHP files such as webshells, and monitor outbound requests tied to plugin promotional or dashboard components. WAF visibility may also be useful; Wordfence said it began seeing attacks on August 7.
BleepingComputer said the WordPress Plugins team closed the affected BdThemes products pending review, and that the poisoned API endpoints had been returning clean JSON by the time of publication. The article also noted that BdThemes had not published an official statement at the time it was written.
The larger lesson is that WordPress hosting security now includes the “quiet” remote services inside plugin dashboards: ad banners, onboarding panels, template libraries and license checks. If those services can write JavaScript into wp-admin, they deserve the same scrutiny as update servers and package repositories.
Source: BleepingComputer — “BdThemes plugins supply-chain hack creates rogue WordPress admins”.